Security
Security built into the product
Scenovix holds match video, results and the accounts of your team. Every measure on this page is part of the product today, explained in plain words.
01
Accounts and sign-in
Strong defaults for every person who signs in, whether with a password or with your identity provider.
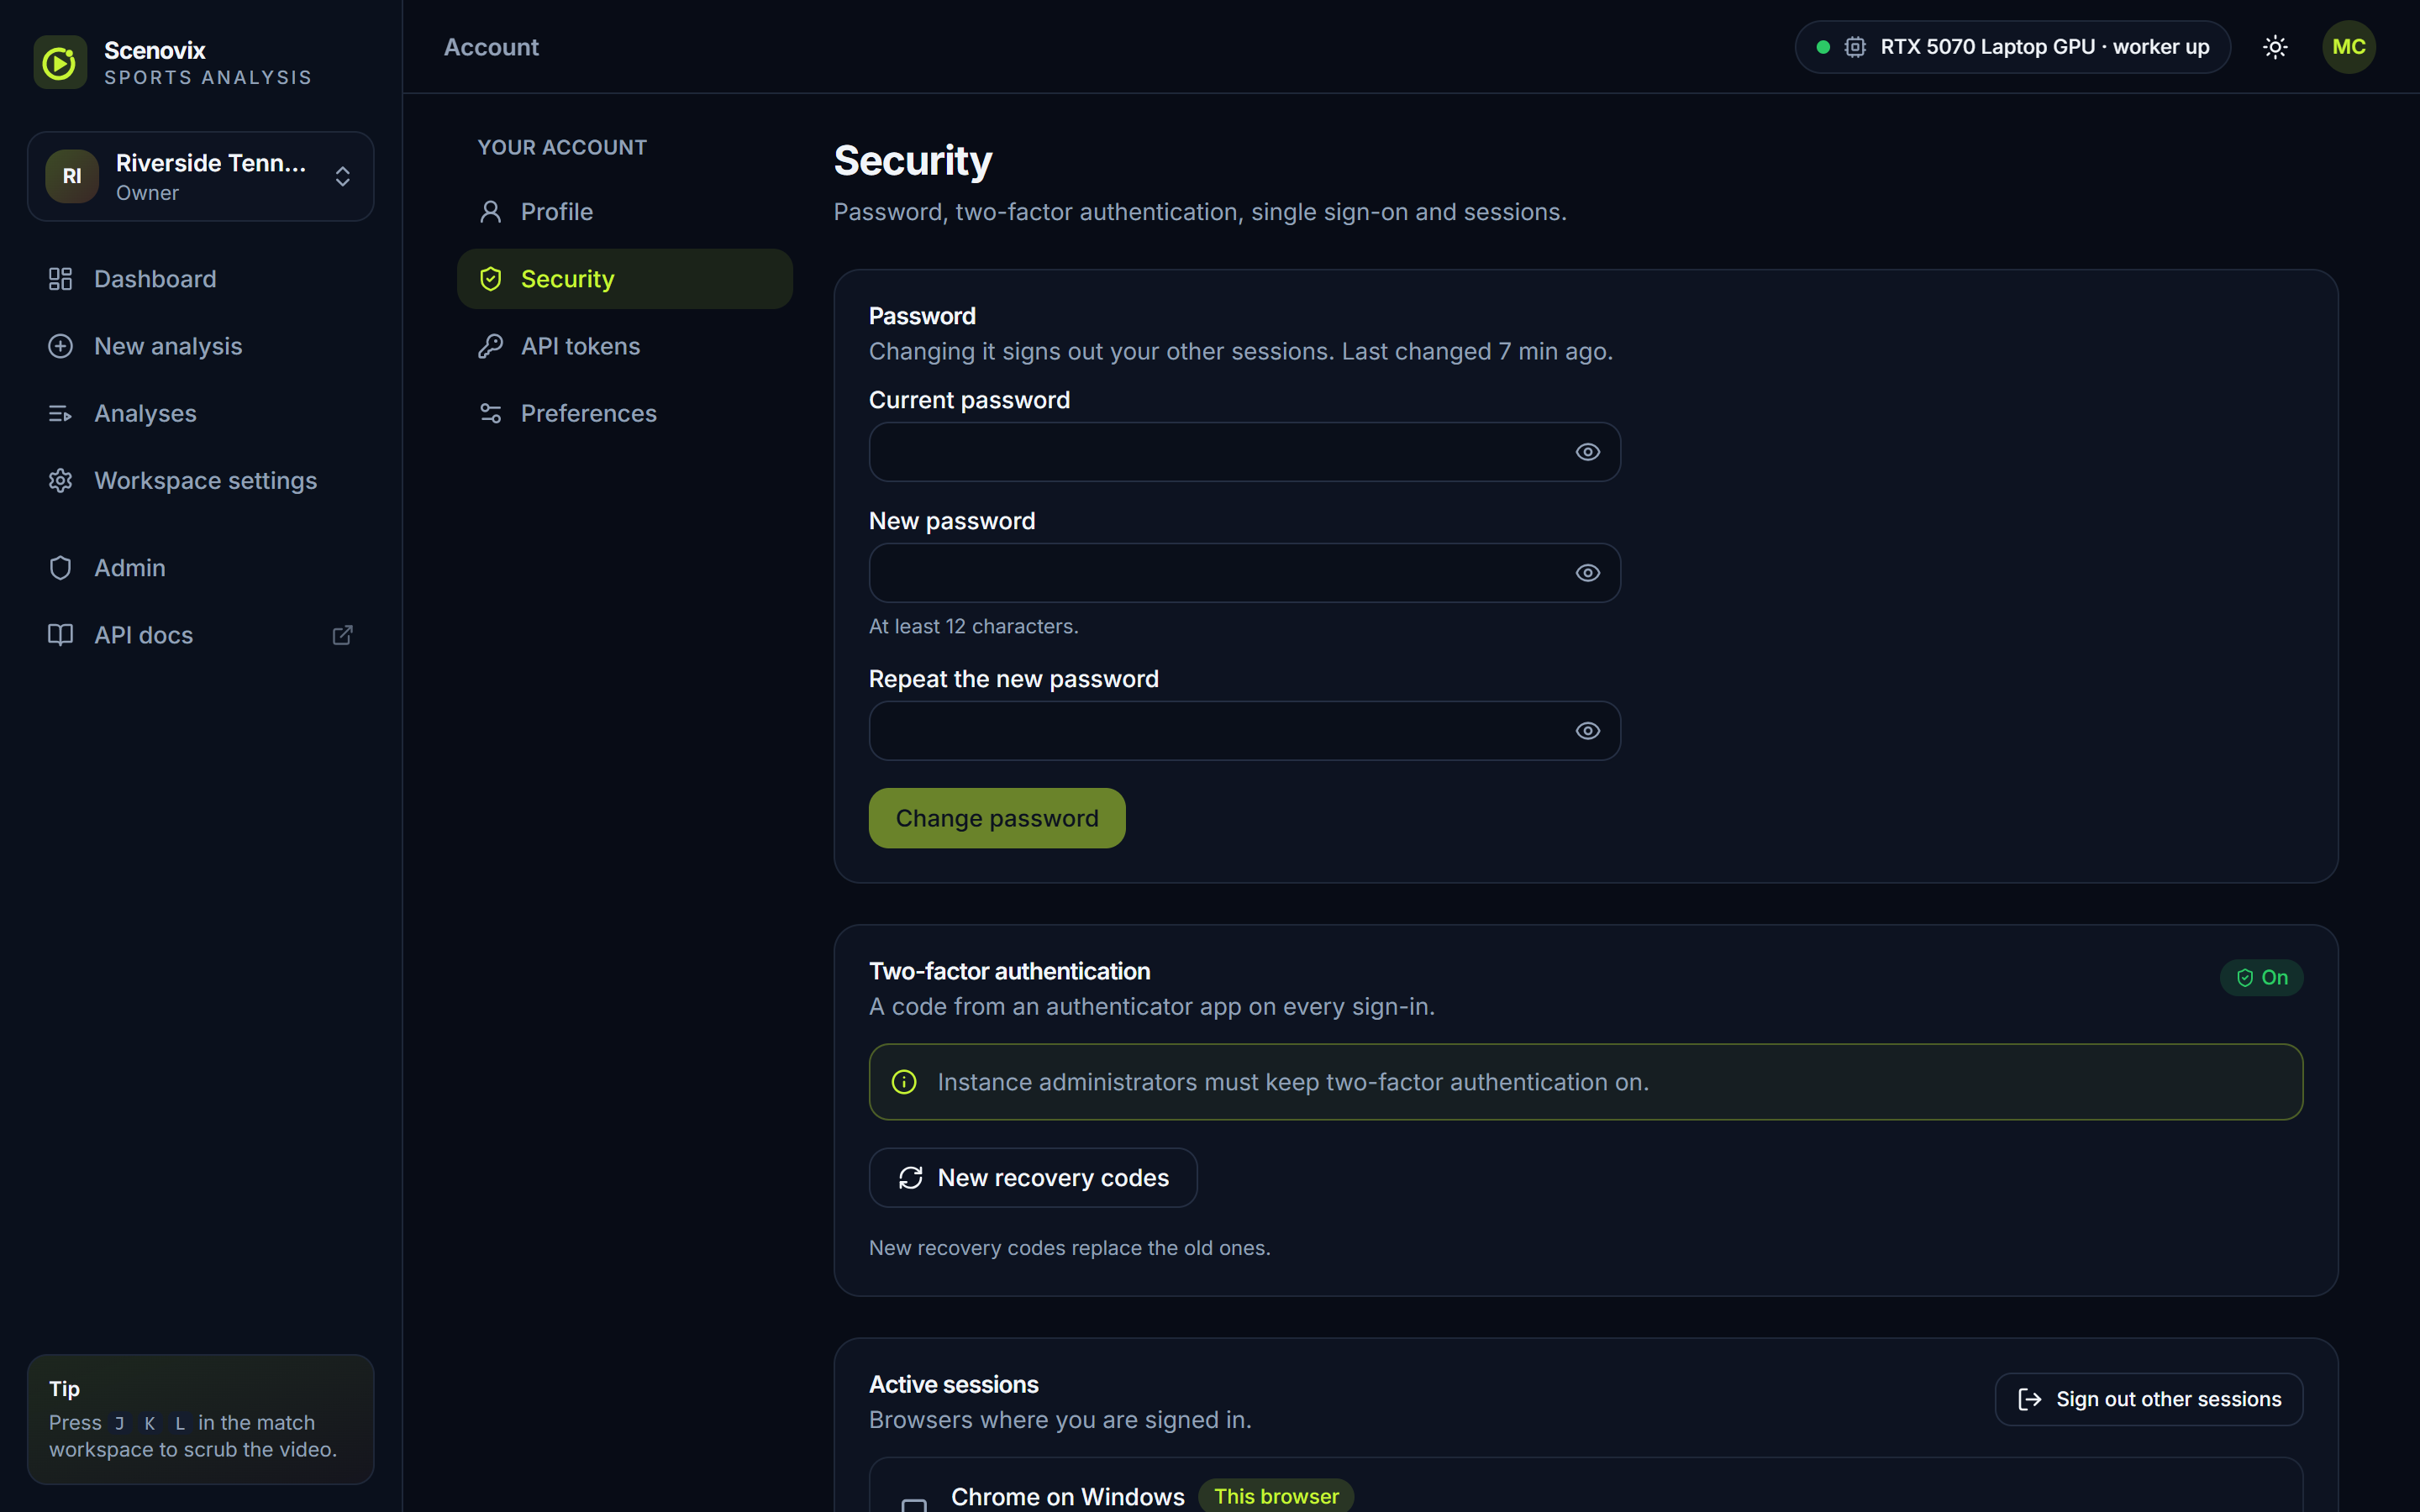
argon2id password hashing
Passwords are never stored. We keep an argon2id hash, a slow, memory-hard algorithm built to resist cracking, and rehash automatically when the parameters change.
Common password checks
New passwords need at least 12 characters and are refused if they appear in a list of common passwords or contain your name or email address.
Two-factor authentication
Time-based codes from any authenticator app, plus ten single-use recovery codes. Each code works only once, so an observed code cannot be replayed. Workspaces can require 2FA for every member.
Single sign-on with OpenID Connect
Sign in with your organisation's identity provider, such as Google or Microsoft. The flow uses PKCE, state and nonce checks, and verifies every ID token. Workspaces can require SSO.
Rate limits and backoff
Repeated failed sign-ins slow down exponentially per account and per IP address, and sign-up, password reset and invitations are rate limited. Unknown accounts get the same answer, in the same time, as real ones.
02
Access control
People and integrations get exactly the access they need, inside one workspace at a time.
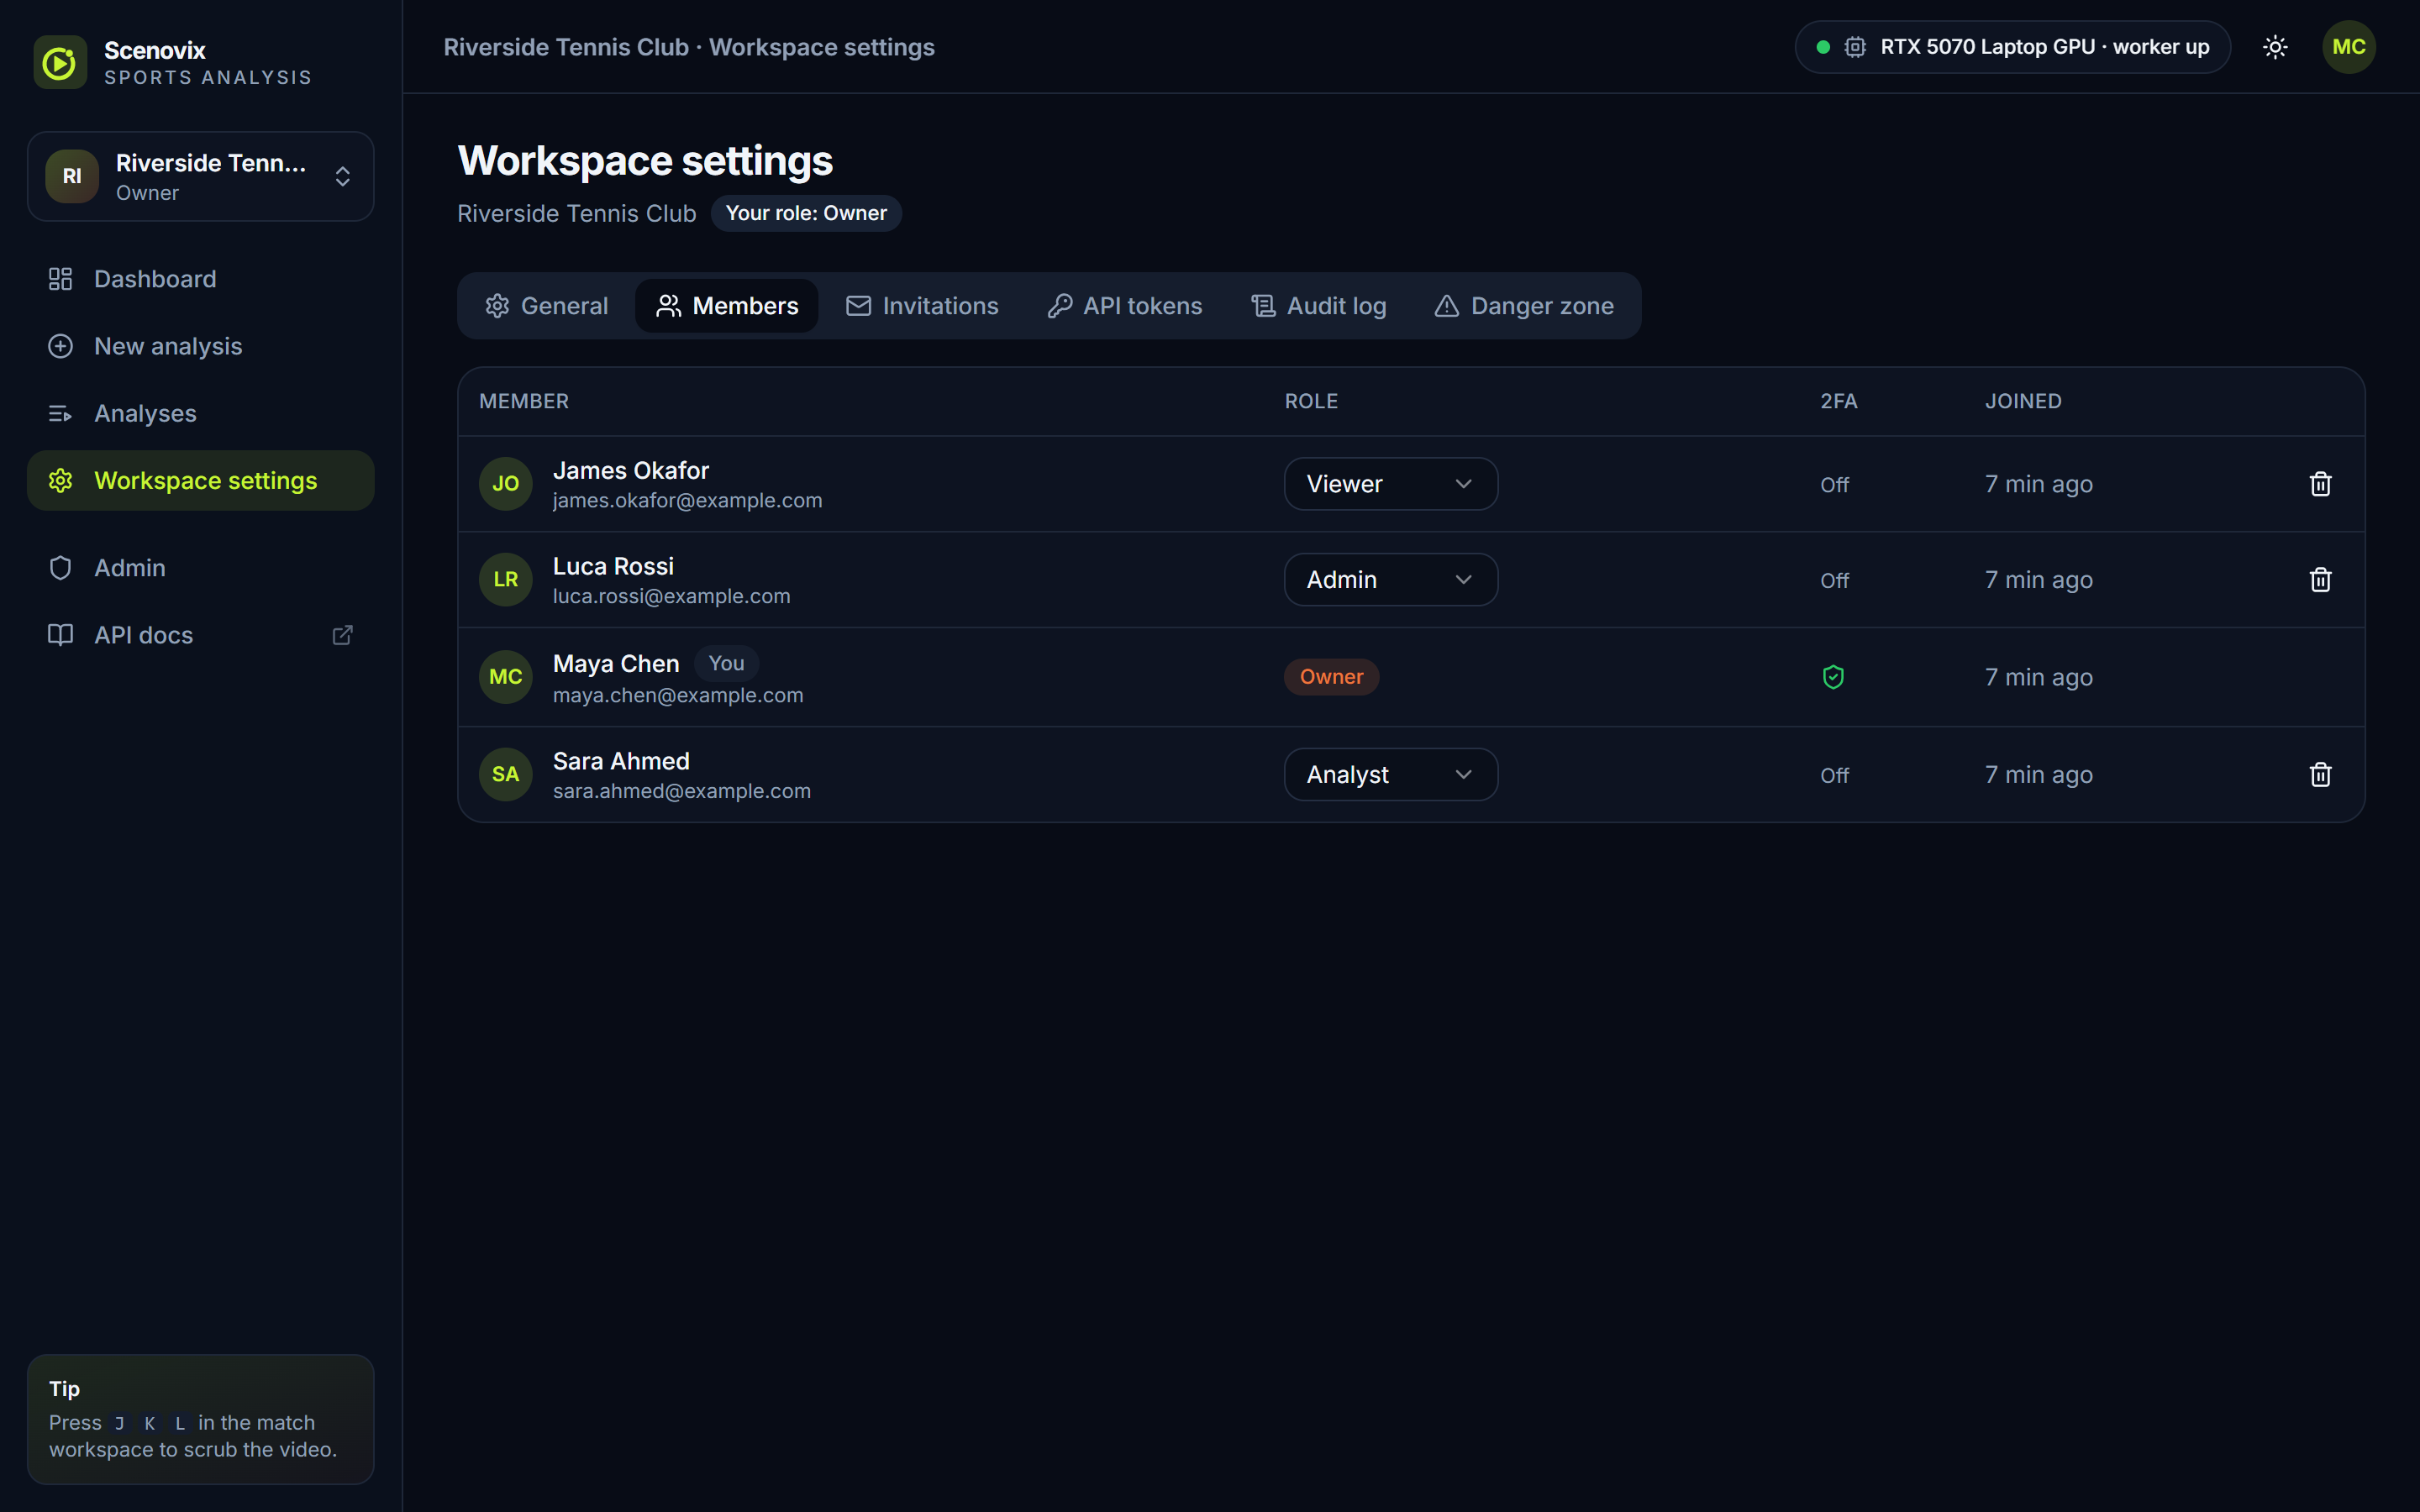
Workspace roles and permissions
Every member has a role in each workspace: owner, admin, analyst or viewer. Each role maps to explicit permissions, checked by the server on every request. People outside a workspace cannot even confirm that its analyses exist.
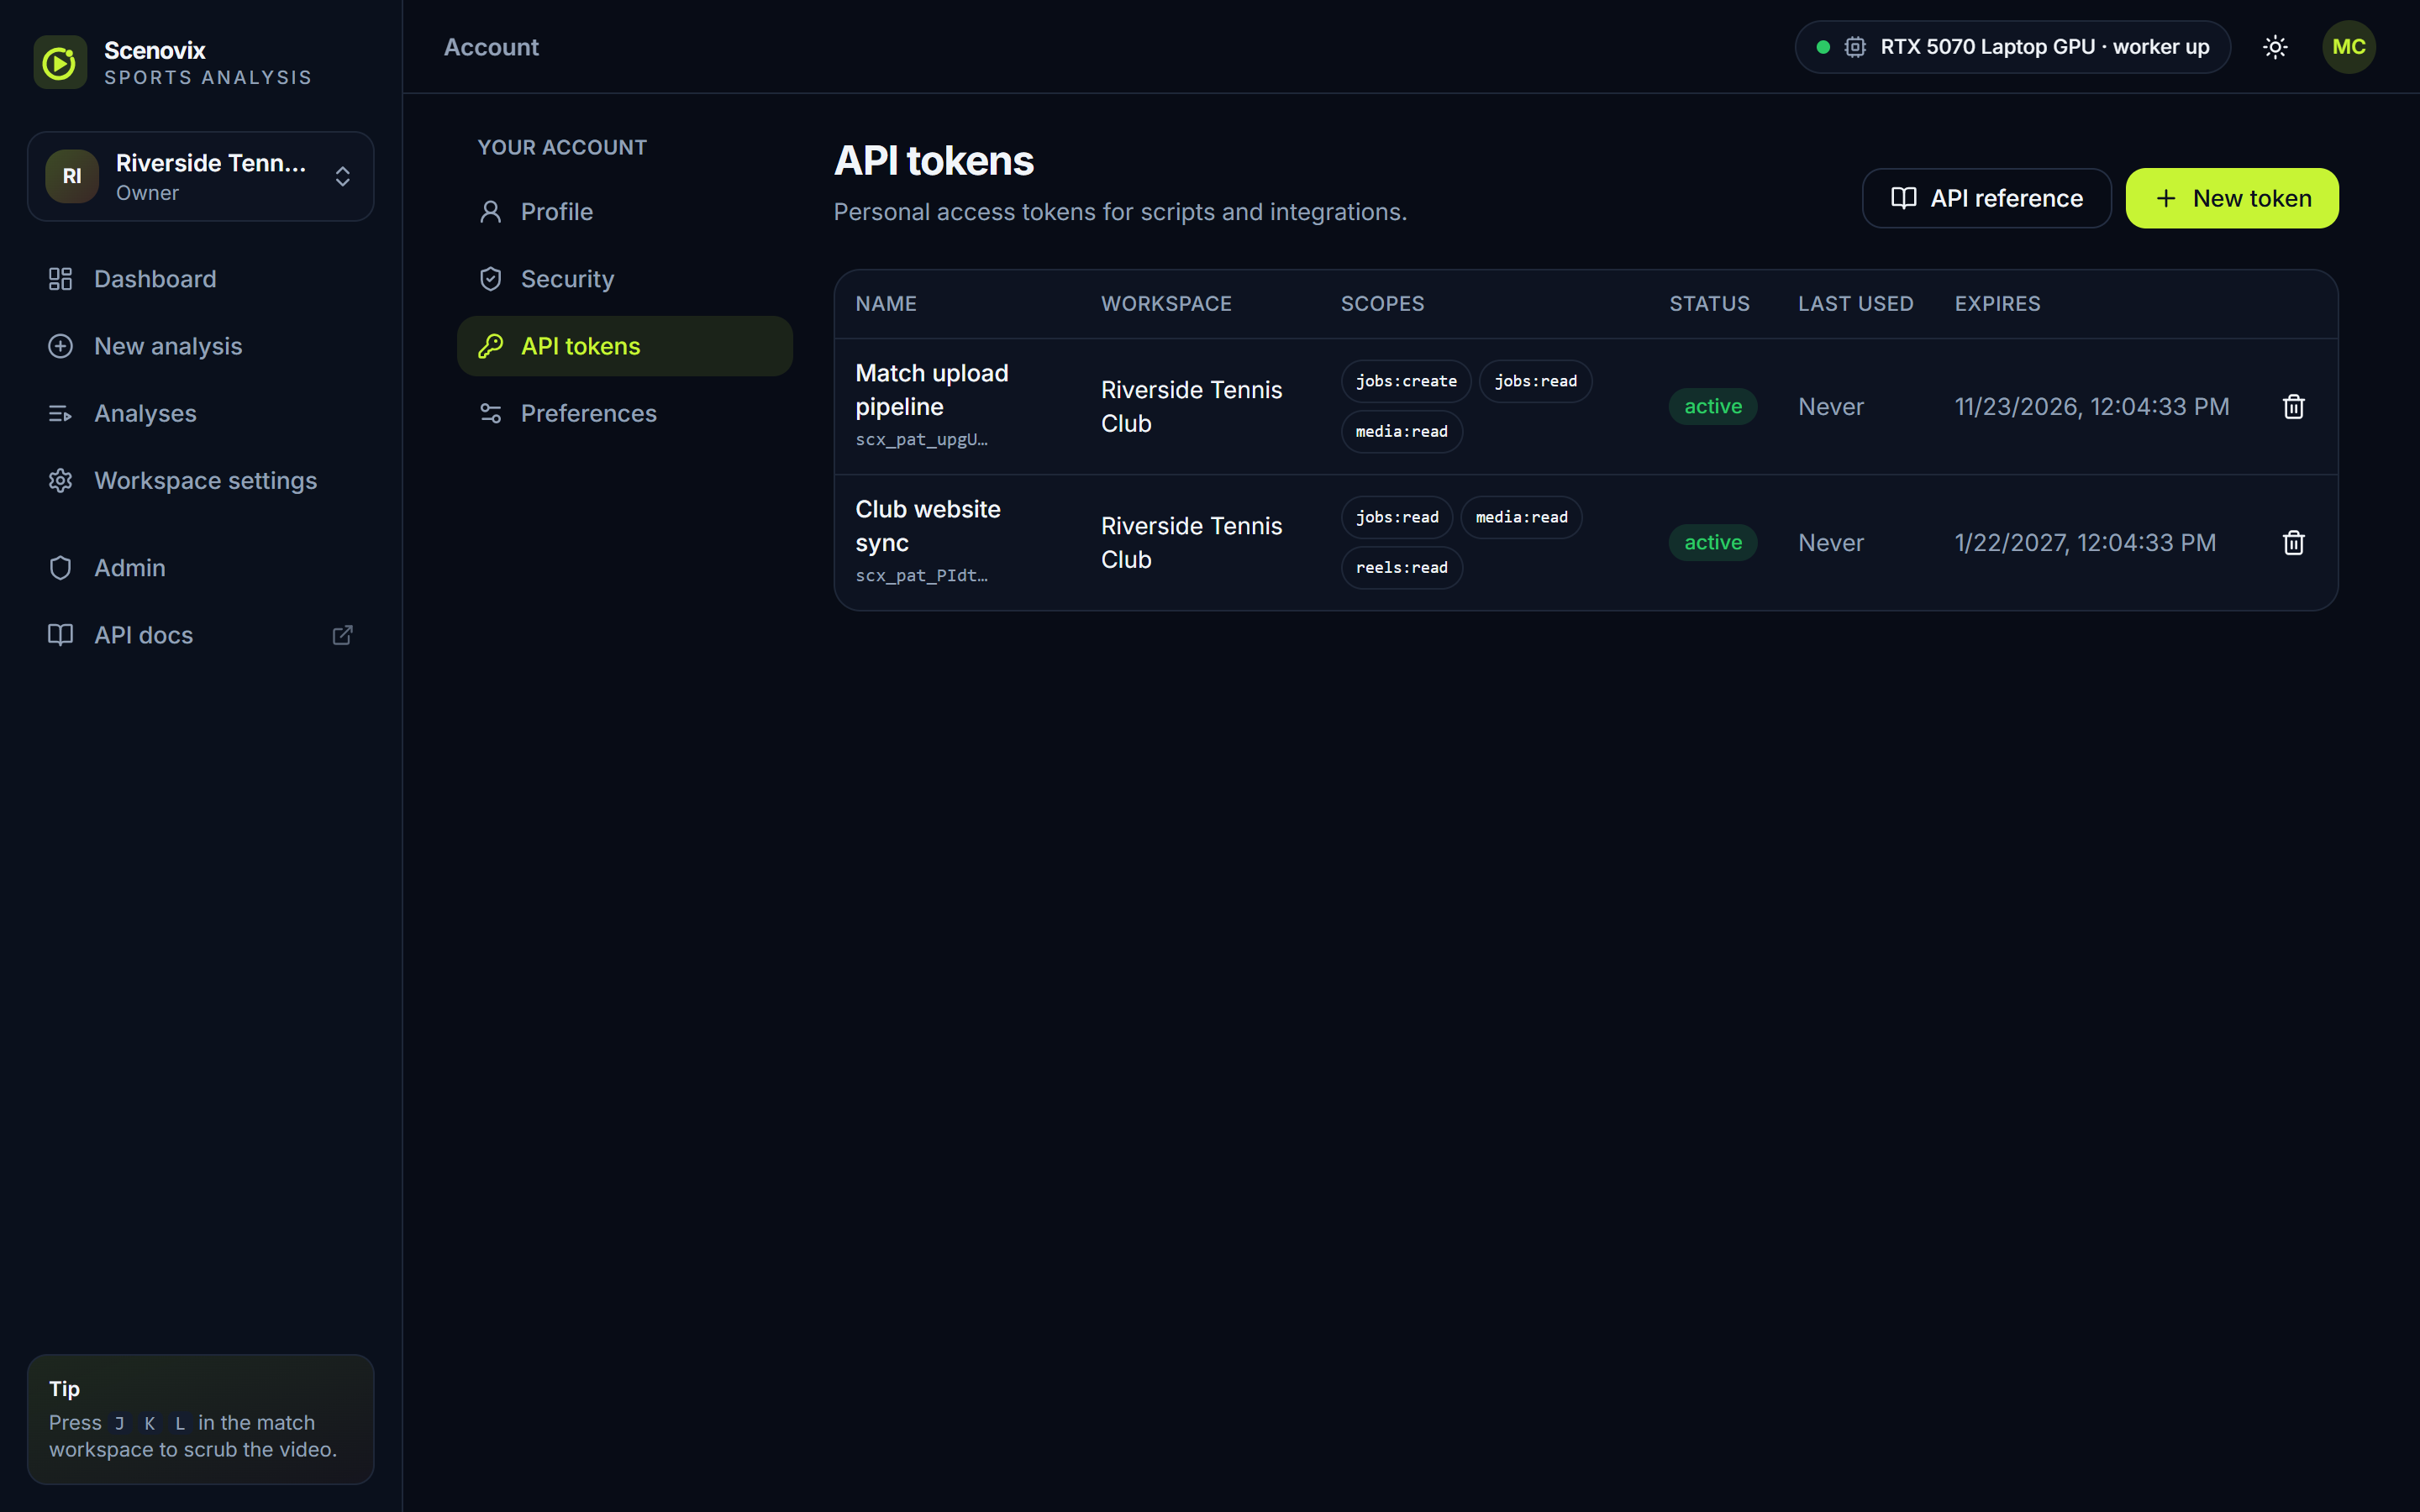
Scoped, workspace-bound API tokens
Tokens for scripts and integrations work in one workspace, carry only the scopes you pick, and expire (90 days by default). They never exceed their owner's current role, are shown once and stored only as a hash. Revoke them any time.
Re-authentication for sensitive actions
Changing your email, managing 2FA, creating tokens and deleting a workspace or account all ask you to confirm who you are first.
03
Visibility and data protection
A record you can trust, and secrets that stay protected even if the database is copied.
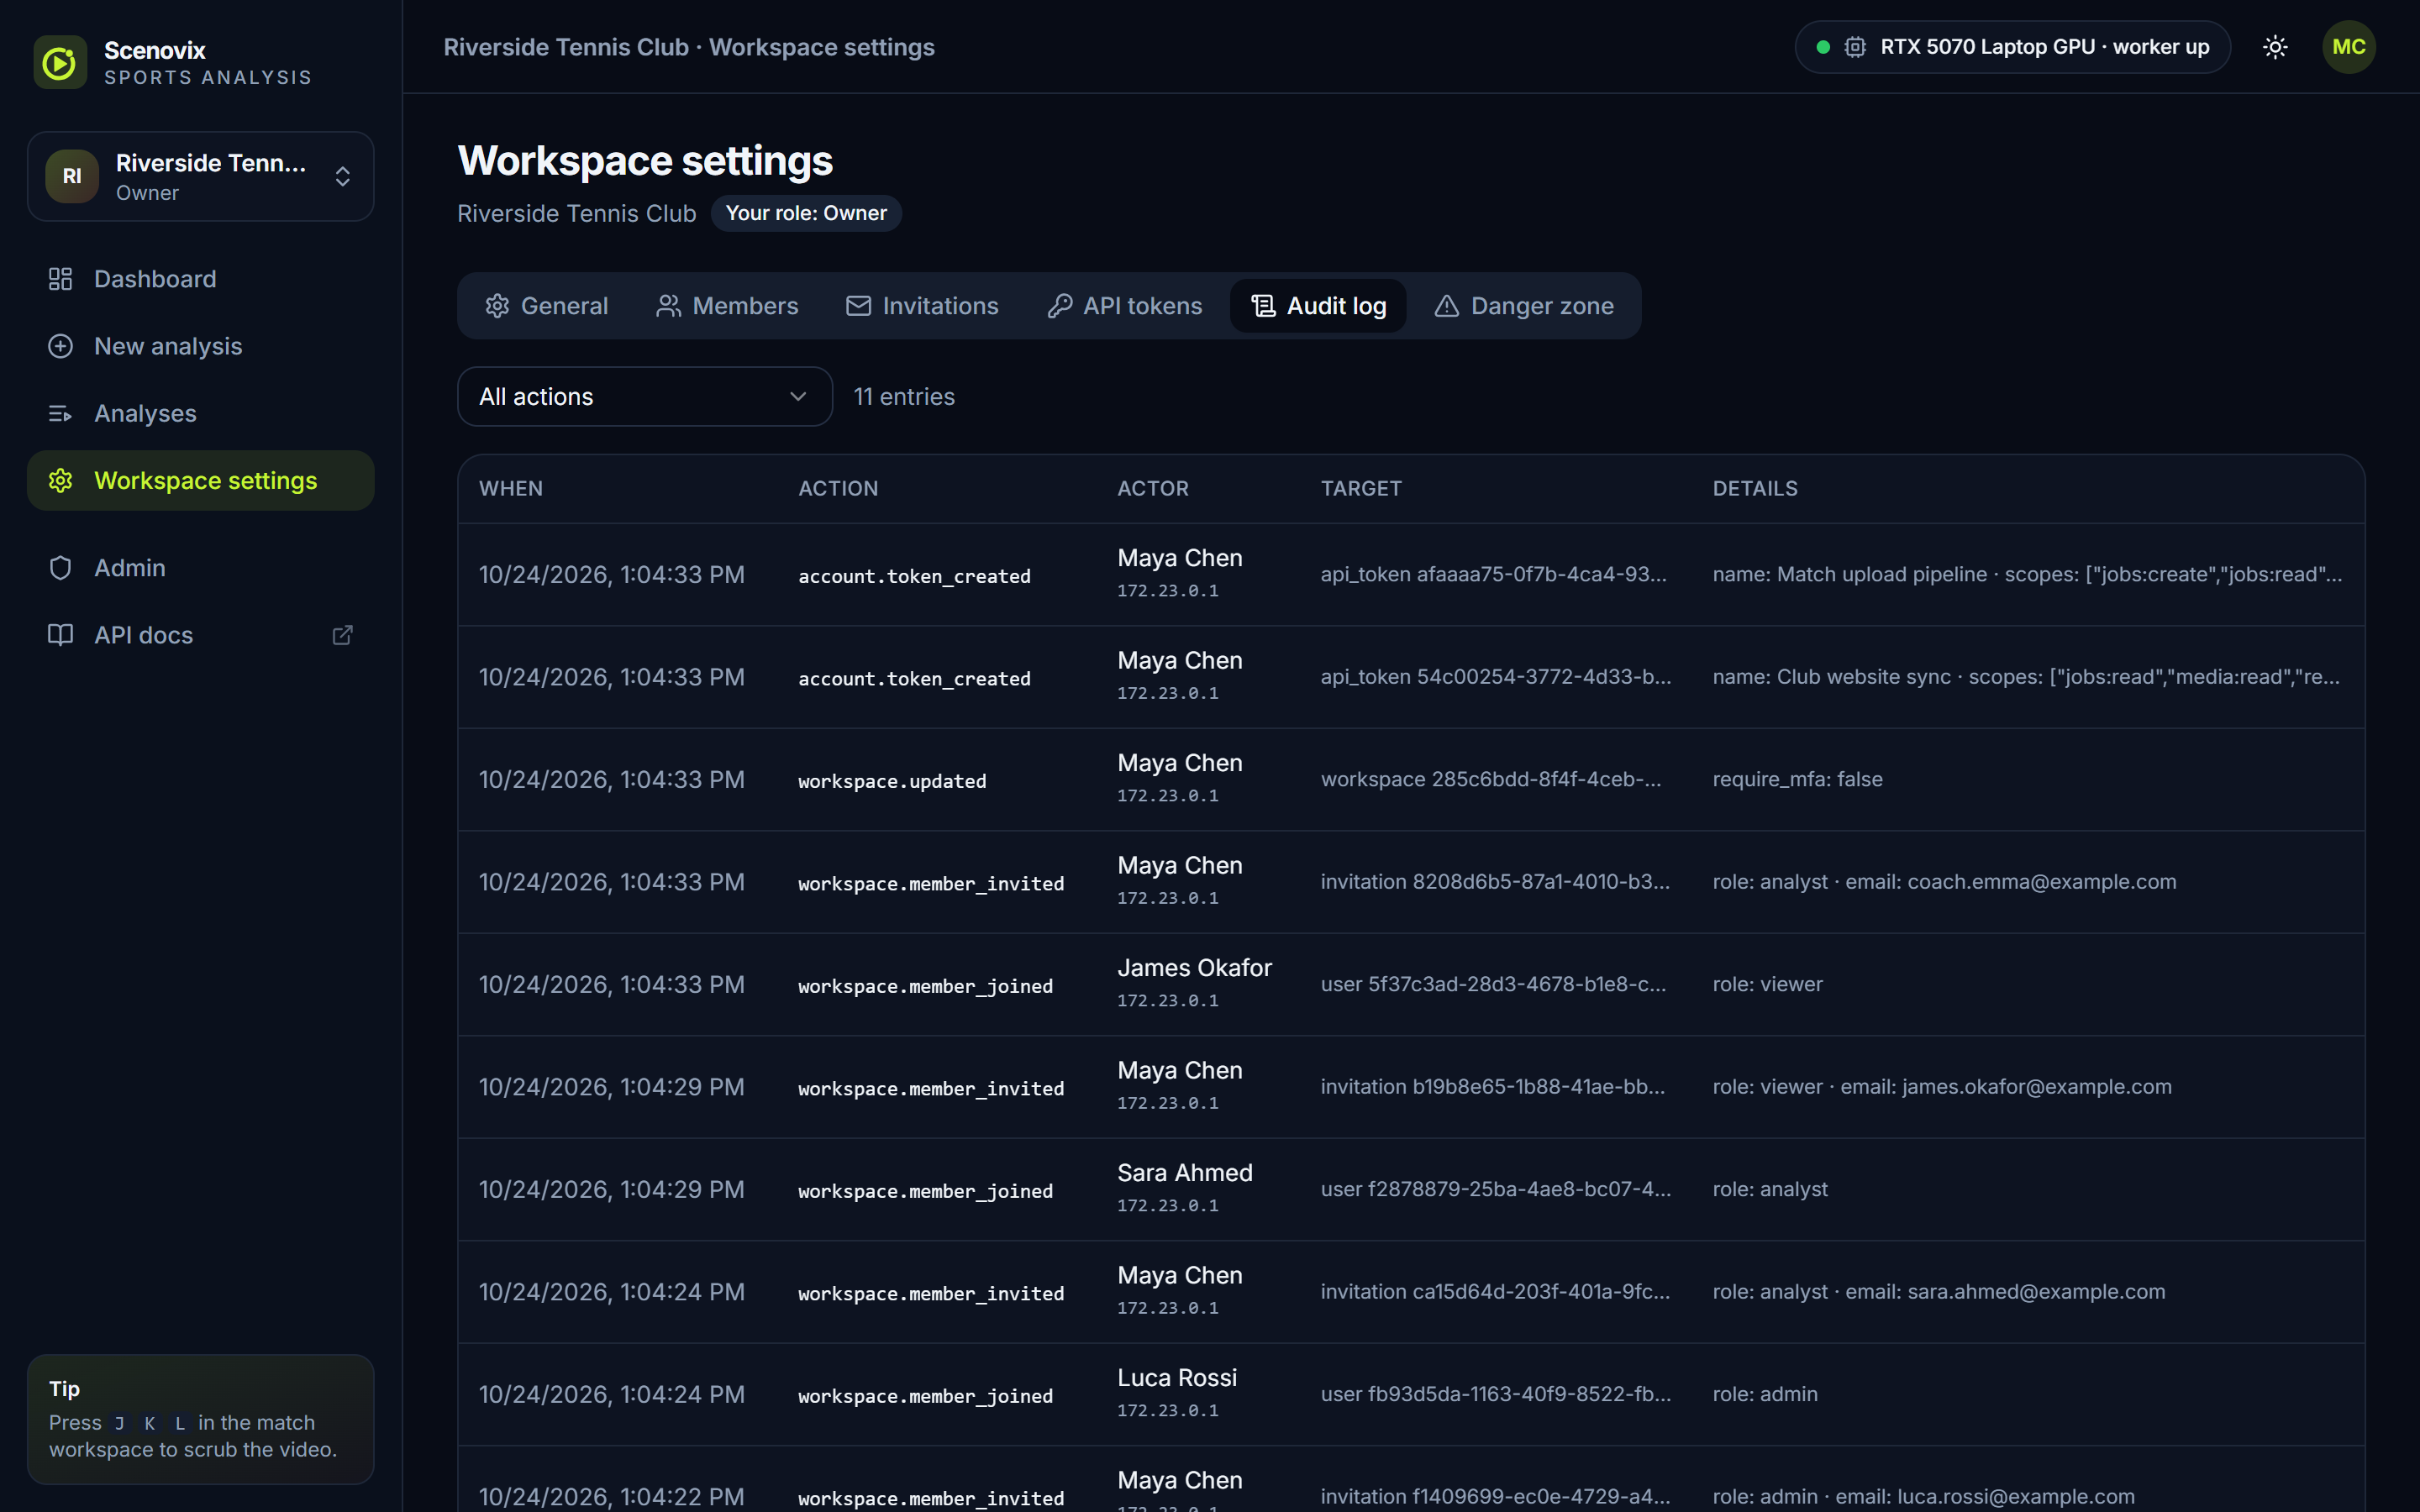
Append-only audit log
Sign-ins, role changes, tokens, invitations, deletions and admin actions are recorded with time, actor, IP address and details. The database refuses edits to the log, even from its owner.
CSRF protection and secure cookies
Browser sessions use an HttpOnly, SameSite cookie, marked Secure over https. Every change made from the browser needs a CSRF token and a trusted origin. Pages are served with a strict Content Security Policy, and with HSTS over https.
Encryption keys with rotation
Two-factor and webhook secrets are encrypted with keys derived for each purpose. Rotate a key by adding a new one in front: older keys keep decrypting until you remove them.
04
Integrations and your data
Safe connections to your systems, and full control over where your data lives and when it goes.
Signed webhooks
Every webhook carries an HMAC-SHA256 signature made with your workspace's own secret, so your server can check that it came from Scenovix. Admins can rotate the secret at any time.
SSRF-safe delivery
Webhooks only go to public addresses. Private, loopback and cloud-metadata targets are refused, the checked address is pinned for the connection and redirects are not followed.
Data deletion and export
Delete an analysis and its files, a workspace with everything in it, or your whole account. Export everything stored about you as JSON whenever you like.
Self-hosting
Run Scenovix on your own servers: one Docker image next to PostgreSQL, so match video and results never leave your infrastructure.
Responsible disclosure
Found a security issue in Scenovix? Please tell us privately first, with enough detail to reproduce it, and give us a reasonable time to fix it before you share it.
Scenovix does not hold security certifications today. If your organisation needs details for a review, get in touch.